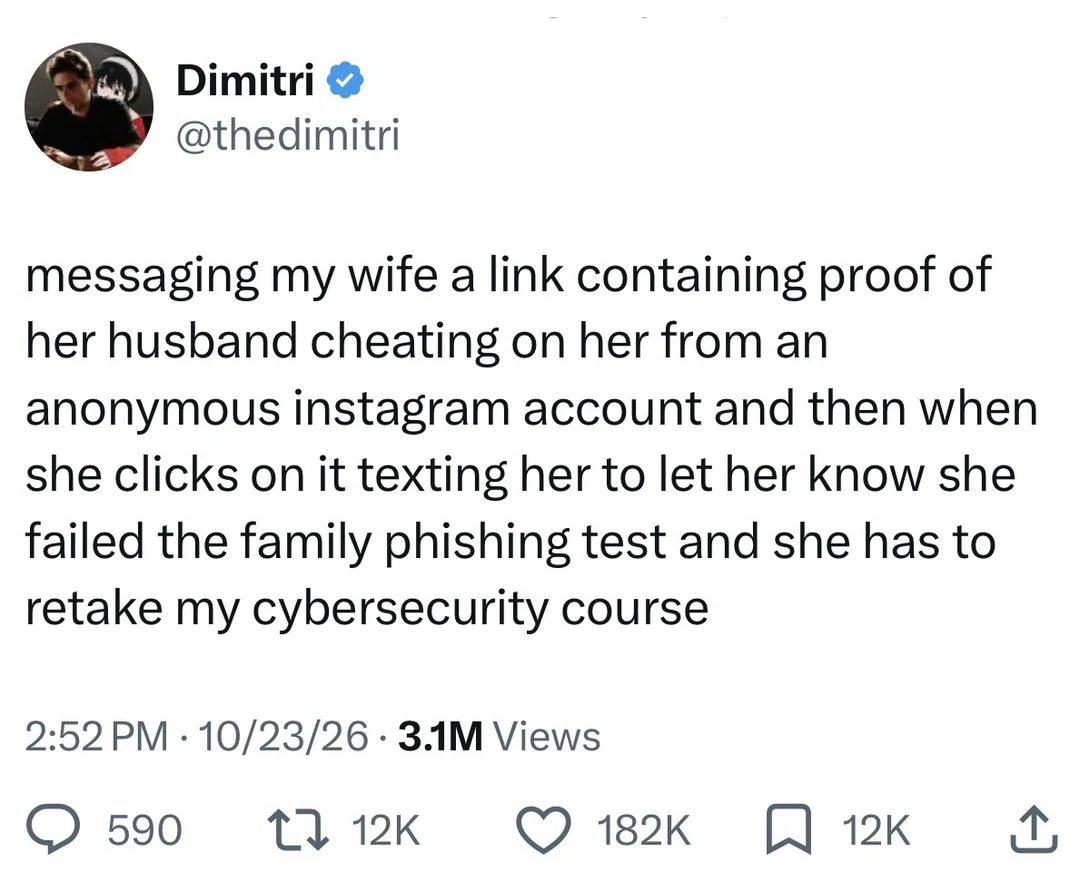
My current company makes it real easy. All their simulated phishing addresses use the fictitious TLD of ".corn" so I just setup an email rule to filter them.
Welcome to Programmer Humor!
This is a place where you can post jokes, memes, humor, etc. related to programming!
For sharing awful code theres also Programming Horror.
My current company makes it real easy. All their simulated phishing addresses use the fictitious TLD of ".corn" so I just setup an email rule to filter them.
I know this is a leap, but for some reason reading this made me want to buy a domain like virus.porn and make it the most wholesome, lemmy community on the planet.
Oh, you mean like penisland.net?
Or girlsof in stagam, which apparently has disappeared but used to be the story of the adventures of a person called Girlsof in the magical realm of Stagram.
I remember that one too, but think it was actually called Slütsof In Stagrâm

Just leaving their bare ass out there with no ssl, smh
It's only one ssl. How much could it possibly cost? 4 dollars?!
I the worst part is deciding which flavor to get

I like that the most expensive one is called "wildcard".
Sounds like it's gonna perform AMAZING feats of security some of the time and just not work at all at other times.
Kinda like the wild mage of encryption 😁
Be the change you want to see! I'll sign up straight away.
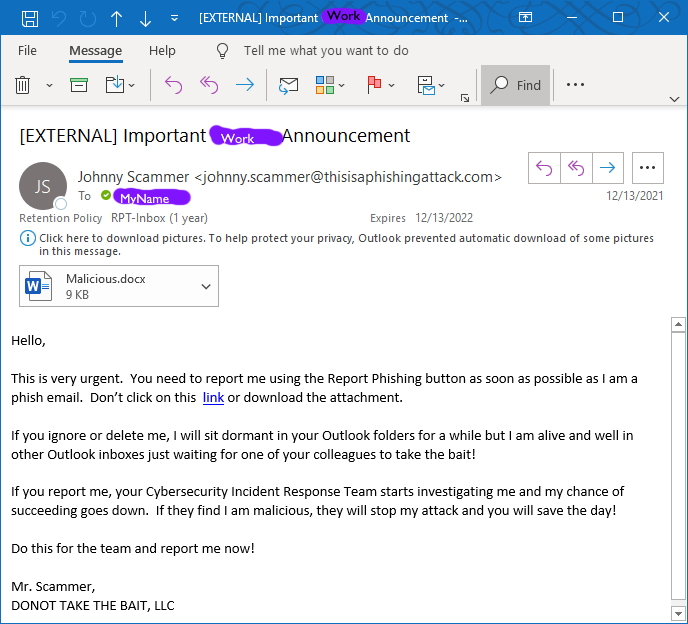
An actual email sent by my company. (not representative of their usual)
That's pretty cool. Gets the point across - and the reason and results of why it matters to report instead of ignore. Kudos to your team.
Yeah if anyone falls for this lock them out of their computer immediately.
Clearly he's trying to trick you into pressing the "Report Phishing" button, which must be some sort of a trap. I'd check the attached document for further clues, especially since he's telling me not to. Must be something interesting there
I delight in reporting genuine emails from my company that look like sophisticated phishing attempts, bonus points if they send a follow-up assuring us that the previous sketchy email was in fact genuine.
A company I was in a few jobs back had several layers of IT department, there was the local studio department that handled our everyday stuff and a "head office" somewhere far away that set policy and handed out budget and whatnot.
One day "head office" IT decided it was a good idea to send out some fake phishing emails to "test" us. They didn't tell the local IT department about it, I guess they were also being "tested". My manager received one and only recognized it as a phishing attempt after he'd clicked just one too many things for it to feel safe to ignore. So he yanked the power on his computer and contacted the local IT department, as is protocol when something potentially dangerous just happened.
The local network went into lockdown while local IT tried to figure out if something actually dangerous had happened. It cost the studio as a whole several hours of work time, which for a studio our size translated to an obscene dollar cost. Nobody on our side of things did anything wrong, even that one extra "dangerous" click my manager did wasn't something he could be blamed for - head office had crafted the fake phishing attempt well and his reaction to it would have prevented damage had it been real.
Head office never tried a stunt like that again.
I've also never fallen for any of the phising emails the IT department sends to test me, my secret is almost never checking my email
My company sends at least one fake phishing email a week. They track stats for them on a security page and I wear it as a badge of honor that my report says 100% viewed and 0% reported.
My company makes you take a course of you fail one or if you ignore 4 or 5 so I have the highest reporting record of the company just because of how much I hate that course
Kemming is 100 level preparedness.
They need to up their game to cover internationalized homograph vulnerabilities, using roughly similar characters from different international alphabets to create totally different domain names:
example.com
exаmple.com
They look identical but are entirely different.
My company is using phishing simulations from a company that puts their company name in the x headers or every email, so that's also easy filter.
As a bonus, that filter also throws all the full security training courses to junk
If your company contracts with phish.me then that URL is actually in the email header metadata.
Just set up a rule for the word phish to a special folder, and then you can use the "report" button on everything in that folder to get the credit.
Mine includes a header so their mail filter knows to ignore it.
At this point, I'm pretty sure that every employee who has been there for more than a month has written or at least copied a filter to delete any email with that header.
I've never been comfortable with that kind of mass deletion and we have, AFAIK, unlimited mailbox storage, so I just set my version to mark those emails as read.
edit: Mail, not mark.
My knee jerk reaction is to calmly explain why this isn't appropriate in a corporate environment.
I'm so broken.
Just read this to a beautiful woman I know.
Her response: That's not going to end near as well/funny as you think/hope it will.
Neither is your future if your wife maintains such easily exploited vulnerabilities.
Blink 8 times if you're in danger
I failed one of those because I have script blockers on my browser and I wanted to see what the scam was.
The URL is likely unique to identify you as soon as you have clicked.
Same, script blocker, virtual machine, etc. Found that apparently you are not meant to forward/report the scam to IT either.
Moral of story: Never inform the company of any suspicious behavior; just ignore it.
There's a button that says report phishing for many companies
some phishing emails also have a button like that, very funny
Sounds kinda like the Tale of Foolish Curiosity from Don Quixote. Spoiler: the wife was a good woman and wouldn't have cheated on the guy... until he started being an asshole by subjecting her to endless tests to prove her virtue.
I saw one with a bunch of maga triggers. The Democrats are doing what!? 😱 they click every time.
May their PCs be infected and their accounts be emptied.
Note that at no point does he claim this "proof" is falsified.
I've set my last name in caps. So any IT Phishing script using a just sends my name in caps. And then I just set up a filter.
They should really try and make them more believable
Just don't read the mails and you won't get fished
My work email is a .edu, and so most of ours are just social media phishing attempts with fake IG and Tiktok links. But why I'm the world would you use .edu for those?
You wanna target .edu, do a quick check on our publicly accessible faculty pages and pretend to be us. I swear, we've got like zero protection against that, lol.
Hey Barb, I forgot my keys, please leave the garage open. Thanks, Jeff.
Boom, stole the faculty coffee maker.
His wife is not Italian. If she was he would not even dare to do anything of the sort.