If you run an exe expecting it to be a movie you kind of deserve it.
this post was submitted on 17 Sep 2026
52 points (100.0% liked)
Piracy: ꜱᴀɪʟ ᴛʜᴇ ʜɪɢʜ ꜱᴇᴀꜱ
70631 readers
336 users here now
⚓ Dedicated to the discussion of digital piracy, including ethical problems and legal advancements.
Rules • Full Version
1. Posts must be related to the discussion of digital piracy
2. Don't request invites, trade, sell, or self-promote
3. Don't request or link to specific pirated titles, including DMs
4. Don't submit low-quality posts, be entitled, or harass others
Loot, Pillage, & Plunder
We heartily recommend visiting the free port of freemediaheckyeah (aka FMHY) while you sail the high seas, for all the freshest links the ocean has to offer.

📜 c/Piracy Wiki (Community Edition):
🏴☠️ Other communities
FUCK ADOBE!
Torrenting/P2P:
- !seedboxes@lemmy.dbzer0.com
- !trackers@lemmy.dbzer0.com
- !qbittorrent@lemmy.dbzer0.com
- !libretorrent@lemmy.dbzer0.com
- !soulseek@lemmy.dbzer0.com
Gaming:
- !steamdeckpirates@lemmy.dbzer0.com
- !newyuzupiracy@lemmy.dbzer0.com
- !switchpirates@lemmy.dbzer0.com
- !3dspiracy@lemmy.dbzer0.com
- !retropirates@lemmy.dbzer0.com
💰 Please help cover server costs.
 |
 |
|---|---|
| Ko-fi | Liberapay |
founded 3 years ago
MODERATORS
windows hides file extensions by default.
I still don't get why this is the default, and why people don't change it when they install. It's been a detriment of the OS since day one, and changing that one thing alone probably could have saved so many people over the decades.
You can change it??
I think it's in the view menu, or in folder options somewhere. I only really use Windows at work these days so I can't check it right now. But yeah, you can turn on extensions. It used to be one of the first things I did on a Windows install.
DOS making file extensions a fundamental part of their filesystem just to hide them by default in windows is some good irony.
So unhide them? It will still say Application under type. I’m not going to defend Microsoft doing that but it’s not like it’s a new thing or it’s hard to fix.
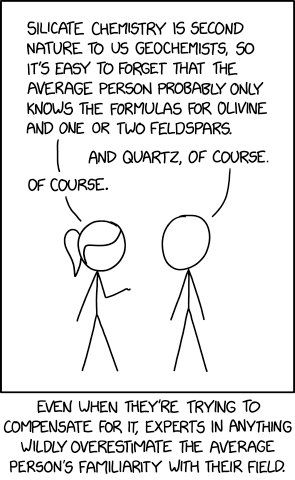
Sure, but this isn’t geochemistry it’s the most popular desktop OS in the world that the person in this scenario ostensibly owns and uses. In addition, they’re using it for the famously risky practice of piracy so you’d expect a modicum of caution.
You've never ever played tech support for a relative. I can tell.
I absolutely have, and if they infected themselves with The.Odyssey.2026.1080p.AMZN.WEBDL.H265.exe I would absolutely make fun of them.
Thats not very nice of you
Can’t argue that, but hopefully it’d be motivation for them to look at what they’re opening.
I've gotten infections from payloads hidden in MP4 metadata before. It doesn't have to be an exe.
It would be a kinder world if ignorance wasn't exploited / punished.
But, yeah. It's not like malware in movies was the first time that ignorance would be very much the opposite of bliss. Plenty of berries that will give you a bad time if you ignorantly eat them; and some plants (and animals) even use mimicry take advantage of the lack of observation or knowledge.
"deserve" might not be the way I'd put it, but you execute enough movies and bad things will happen to you.
if the site is compromised, the hackers wouldn't need to use .exe
just visiting the site would be enough to get infected, potentially
or even clicking on an itorrents link from 1337x, cuz the latter doesn't host their own torrent files
That kind of browser exploit isn't cheap and this is not the way that it is likely to get used.
fair enough.
although the apparent goal of a hack can also be an obfuscation of the true goal which may be more worthy of expense.
whatever though. i accept the community feels I'm overreacting.
fwiw I've always avoided .exe in torrents. maybe why i thought that was a basic b level safety warning.
Avoiding executables from untrusted sources is pretty reasonable.
Well if visiting a (compromised) site can get you infected the problem is not the site, but your browser, right?
i know that's a figurative way of emphasizing things in a certain way. but it's better to acknowledge that both things are problems.
Sure except they did use a .exe. The article states the expected .torrent was being replaced with a .torrent that downloads an 865 MB .exe file.
